

How to Write a Privacy Policy
Learn how to write a comprehensive privacy policy that protects your business and builds customer trust. Step-by-step guide covering data collection, usage, pro...
13 min read
A privacy policy explains how an organization collects, uses, shares, stores and protects personal information. For an affiliate website or program, it should describe the actual data flows behind forms, analytics, referral tracking and commission administration.
On this page
A privacy policy explains how an organization collects, uses, shares, stores and protects personal information. For an affiliate website or program, it should describe the actual data flows behind forms, analytics, referral tracking and commission administration.
The policy gives visitors a way to understand those practices and contact the organization. It should reflect what happens on the site, rather than promises copied from a template.

Set up advanced tracking in minutes. No credit card required.
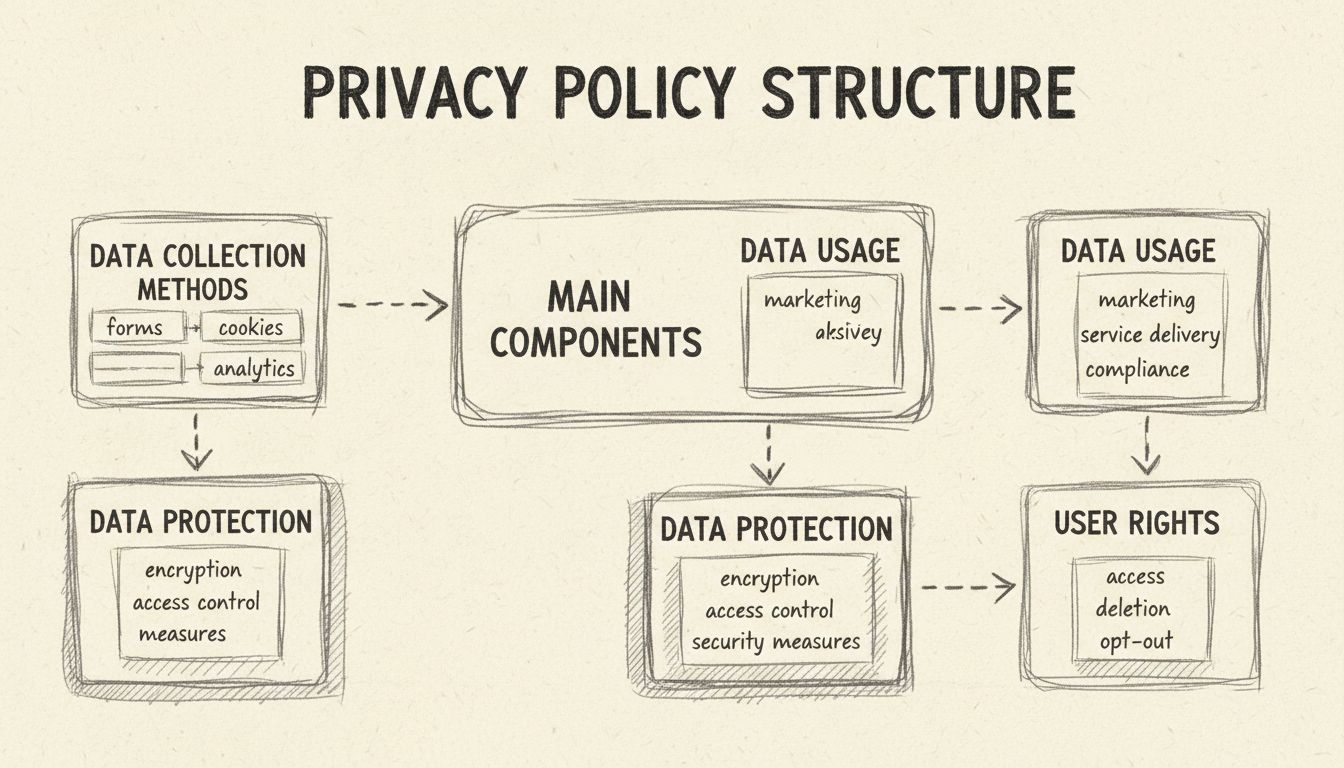
Start with a data inventory. Identify the information collected, its purpose, the organizations that receive it, retention arrangements and the contact responsible for privacy questions. Explain applicable visitor rights and how a person can exercise them.
For example, a merchant might record a referral identifier, an order identifier and the commission amount to reconcile an affiliate sale. A publisher might collect newsletter signups while an external merchant separately processes purchases. Those are different activities and should not be described as though the publisher controls the merchant’s checkout.
Include the tracking technologies actually used. A first-party cookie, a third-party cookie and a server-to-server conversion message have different technical properties; none automatically eliminates privacy obligations. Avoid describing all affiliate tracking as anonymous if identifiers can be associated with a person.
A privacy policy addresses personal data. An affiliate disclosure explains a commercial connection behind a recommendation. A page can need both: one does not replace the other.
A publisher reviewing a product should make its commission relationship clear near the recommendation. Its privacy information should separately explain relevant analytics, forms and tracking. An advertiser should document the data shared with its affiliate platform and service providers.
Be the first to know about new features and product updates.
Legal requirements depend on jurisdiction and circumstances. The UK’s ICO guidance on the right to be informed explains transparency requirements under the UK GDPR. It is a jurisdiction-specific reference, not a universal template.
Provide an accessible link to the policy, including near relevant data-collection forms. Review it when tracking methods, service providers, purposes or retention arrangements change. Test whether what the policy says matches the current checkout, newsletter and affiliate tracking workflows.
Templates can help organize a draft, but they cannot establish which laws apply or verify how the business handles data.
Not every privacy policy offers meaningful protection. When reviewing a privacy policy — your own or someone else’s — watch for these warning signs:
Vague sharing statements. A useful policy identifies recipients or recipient categories and explains the purpose of sharing. A phrase such as “trusted partners” gives little practical information by itself.
No opt-out mechanism. A policy that describes data sales or sharing without explaining how to opt out is a red flag.
Excessive data collection. If the policy lists data categories that seem unrelated to the service — a flashlight app that requests location data and contact lists, for example — ask why those categories are needed and how they relate to the service.
You should be able to find an email address, physical address, or contact form.
No mention of user rights. If the policy does not explain how to access, correct, or delete your data, check how the organization handles the rights that apply; silence alone does not establish what its processes are.
Buried or hard-to-find policy. If you cannot locate the privacy policy within a few seconds of landing on the homepage, visitors may struggle to understand its data practices.
There are three common starting points: a generator, a template, or a policy prepared with professional advice. The best choice depends on the complexity of the actual processing, rather than the number of pages on the website.
| Approach | Useful starting point | What still needs checking |
|---|---|---|
| Generator | A questionnaire produces an initial structure | Whether the questions capture every form, tracker, recipient and purpose |
| Template | An editor adapts a document to the business | Every statement about collection, sharing, rights and retention |
| Professional drafting | Complex processing can receive tailored review | Whether the technical inventory and instructions supplied are accurate |
A generator can save drafting time, but cannot inspect the affiliate tracking implementation or decide every applicable legal obligation. A template can identify missing sections, but should not be copied unchanged. Professional advice can help resolve uncertain requirements, particularly where operations involve several jurisdictions or sensitive information.
Start by mapping the systems rather than selecting reassuring wording. Ask the people responsible for analytics, checkout, newsletters, partner recruitment and payouts what information their systems actually receive. Compare their answers with the configuration and vendor documentation. A policy that claims no personal information is collected can be misleading if the site also runs analytics and records identifiable form submissions.
Avoid promising security measures the organization has not implemented. Explain relevant safeguards accurately without exposing sensitive operational details. Retention statements should also reflect a real process: saying that records are deleted after a particular period does not make the deletion happen.
Assign an owner to maintain the document. Store the data inventory and vendor list alongside it so later changes can be reviewed against the same evidence. A new checkout integration or tracking partner can change the policy even when the public website looks the same.
Affiliate marketing can create privacy considerations when click tracking, attribution or commission records contain personal information. When a visitor clicks an affiliate link, the affiliate network or tracking software typically records the click, sets a cookie, and may collect the visitor’s IP address, device information, and browsing activity.
Workflow example: A merchant runs an online store and uses affiliate tracking software. When a visitor lands on the site via an affiliate link, the software sets a first-party cookie. If the visitor makes a purchase within the cookie window — say, 30 days — the software records the sale and attributes it to the referring affiliate. The privacy information should accurately explain this process so the visitor understands why data is being collected and where it goes.
For a publisher, the data inventory should consider:
Practical tip: Many affiliates combine their privacy policy with an affiliate disclosure page. Although both may be relevant, the privacy policy addresses the data side and the disclosure addresses the commercial relationship. Do not conflate the two.
Workflow example: A publisher runs a review site with affiliate links to multiple merchants. The publisher should describe its own tracking and explain the involvement of external merchants or networks. A link does not always set a third-party cookie: redirects, first-party storage and server-to-server integrations differ. Check the implemented workflow rather than assuming a single tracking method.
Program managers sit between advertisers and publishers and are responsible for ensuring that their program’s data practices are documented and communicated. Key considerations include:
Limitations to note: A privacy policy cannot eliminate all privacy risk. If a merchant’s tracking software experiences a data breach, the privacy policy documents what should have happened, but it does not prevent the breach. Similarly, if a publisher fails to disclose affiliate tracking in their own privacy policy, the merchant’s policy does not cover that gap. Each participant should assess its own activities and responsibilities.
Review your privacy policy at least once a year, and update it whenever:
Each update should be dated. For material changes, assess the notice and consent steps that apply rather than assuming a particular notification method is sufficient.
Use a record for each processing activity rather than a single entry labelled “affiliate data.” Partner applications, website analytics, sale attribution and payouts have different purposes and recipients.
For each activity, record:
For example, a merchant might use a referral cookie for attribution and retain transaction records longer for reversals and payout reconciliation. A publisher might collect an email address for its newsletter while the merchant separately processes the purchase. Avoid suggesting that the publisher collects the merchant’s payment data merely because it earns a commission.
On websites, “privacy policy” and “privacy notice” commonly describe the public explanation of data practices. An internal privacy policy can instead describe procedures employees follow. Give visitors a clearly named document explaining the processing that affects them, regardless of the terminology chosen.
The public document should match internal procedures. If it gives a contact address, someone should monitor it. If it describes an access or deletion process, staff should know how to carry it out. Publishing a notice does not implement consent controls, restrict access or establish a lawful processing basis by itself.
Make the document available near relevant collection points as well as through navigation or the footer. Check account registration, affiliate applications, newsletter forms and mobile views. A footer link can be useful, but a person filling out a form should not have to search the whole site to learn why information is requested.
Learn how to create a robust privacy policy for your affiliate marketing website and ensure compliance with key data regulations.
Learn how to write a comprehensive privacy policy that protects your business and builds customer trust. Step-by-step guide covering data collection, usage, pro...
Discover why privacy policies are essential for your business. Learn about legal compliance, customer trust, data protection, and how PostAffiliatePro helps you...
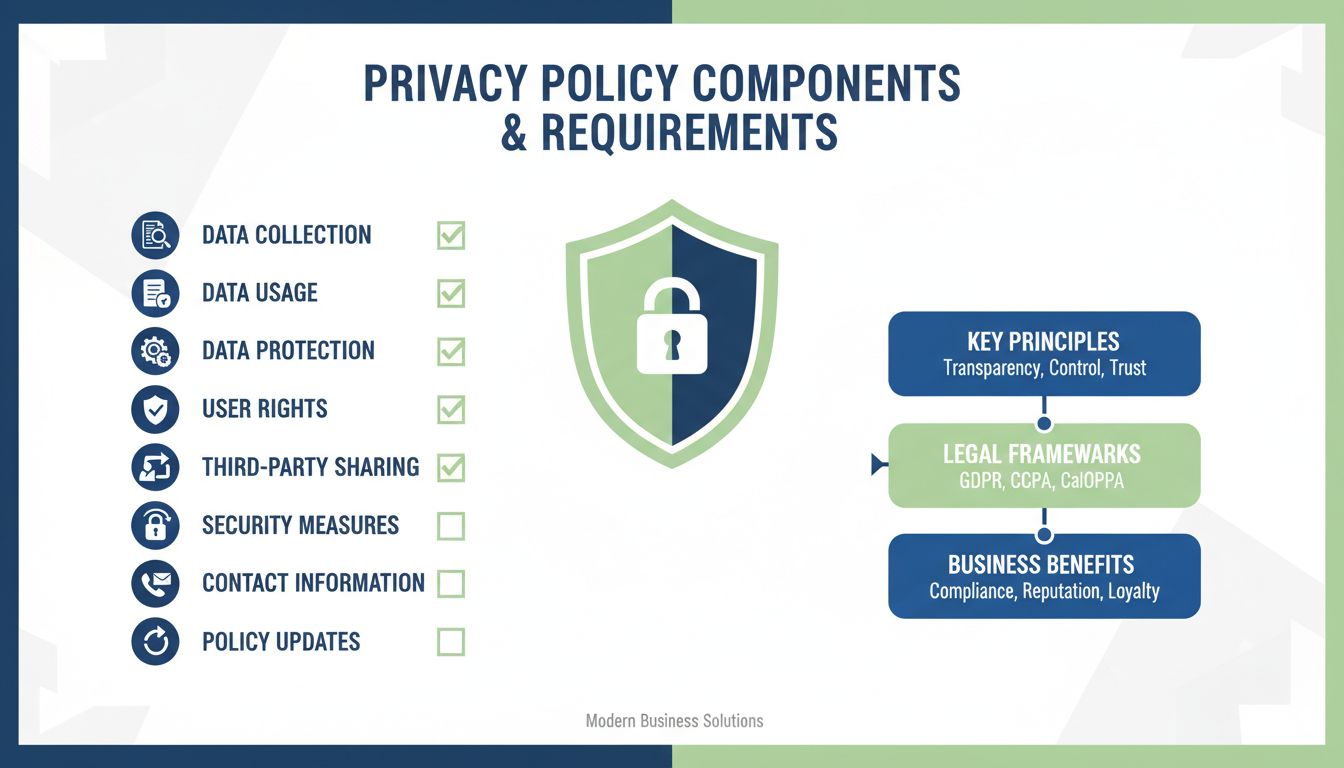
Learn what essential elements must be included in a privacy policy to comply with GDPR, CCPA, and other regulations. Comprehensive guide for 2025.
Join our community of happy clients and provide excellent customer support with Post Affiliate Pro.
Cookie Consent
We use cookies to enhance your browsing experience and analyze our traffic. See our privacy policy.